GraphQL API Testing - Schema Validation, Resolvers, Queries and Performance
Table of Contents
- Introduction
- Understanding GraphQL Testing Challenges
- Schema Testing and Validation
- Testing Queries and Mutations
- Testing Resolvers in Isolation
- Error Handling and Edge Cases
- Performance and N+1 Query Testing
- Security Considerations
- Automation Strategies
- Real World Example
- Conclusion
- Key Takeaways
- Frequently Asked Questions
Introduction
GraphQL has fundamentally changed how clients interact with APIs by allowing them to request exactly the data they need. While this flexibility is a huge win for frontend teams, it introduces unique testing challenges that traditional REST API testing approaches don't fully address. Unlike REST where each endpoint returns a fixed structure, GraphQL exposes a single endpoint with a strongly-typed schema that clients can query in countless ways.
This guide walks through a practical approach to testing GraphQL APIs, covering schema validation, resolver logic, query/mutation testing, performance concerns like the N+1 problem, and strategies to automate your tests effectively.
Understanding GraphQL Testing Challenges
Testing GraphQL APIs requires thinking differently than testing REST endpoints. Here are the key challenges you'll encounter:
- Single endpoint complexity: All operations go through one endpoint, making it harder to isolate and test specific functionality
- Flexible querying: Clients can request nested data, partial fields, or combine unrelated data in one query
- Schema-driven design: The schema is the contract, so changes can have wide-reaching impacts
- Resolver complexity: Business logic is distributed across resolvers, requiring both unit and integration testing
- Performance pitfalls: Deeply nested queries can trigger N+1 problems and excessive database calls
- Authorization intricacies: Field-level permissions add another layer of complexity
Note: The flexibility of GraphQL is powerful, but it also means your tests need to be more comprehensive to catch issues that might only appear with specific query patterns.
Schema Testing and Validation
The GraphQL schema serves as the single source of truth for your API. Testing the schema ensures it remains valid, consistent, and backward compatible.
What to Test
| Test Type | Purpose | Example |
|---|---|---|
| Schema syntax validation | Ensure the schema is valid SDL | Parse the schema without errors |
| Type coverage | Verify all required types exist | Check that all referenced types are defined |
| Deprecation handling | Ensure deprecated fields are marked and alternatives exist | Validate @deprecated directives with reasons |
| Backward compatibility | Catch breaking changes before deployment | Compare schema versions for removed/changed types |
| Directive validation | Ensure custom directives are properly defined and used | Test auth, rate limiting, or custom directives |
Tools for Schema Testing
- GraphQL Inspector: Compare schemas and detect breaking changes
- Apollo Studio: Provides schema validation and change tracking
- graphql-schema-linter: Enforce schema conventions and best practices
# Example of a well-structured schema with deprecation
type User {
  id: ID!
  name: String!
  email: String @deprecated(reason: "Use contactEmail instead")
  contactEmail: String!
}
Testing Queries and Mutations
Queries and mutations are the core operations in GraphQL. Testing them ensures the API behaves correctly for different use cases.
Query Testing Strategies
- Basic field retrieval: Test that simple queries return expected fields
- Nested queries: Verify relationships are resolved correctly
- Filtering and pagination: Test arguments like
where,limit,offset, or cursor-based pagination - Fragments: Ensure reusable fragments work as expected
- Alias and variable usage: Test query flexibility features
Mutation Testing Strategies
- Create operations: Verify new records are created with correct data
- Update operations: Test partial and full updates
- Delete operations: Ensure deletion works and cascades properly
- Input validation: Test with invalid inputs to verify error handling
- Idempotency: For critical operations, test repeated calls
// Example test using Jest and Apollo Server testing utilities
const { ApolloServer } = require('@apollo/server');
const { gql } = require('graphql-tag');

const query = gql`
  query GetUser($id: ID!) {
    user(id: $id) {
      id
      name
      posts {
        title
        createdAt
      }
    }
  }
`;

test('fetches user with posts', async () => {
  const server = new ApolloServer({ typeDefs, resolvers });
  const result = await server.executeOperation({
    query,
    variables: { id: '123' }
  });

  expect(result.body.kind).toBe('single');
  expect(result.body.singleResult.errors).toBeUndefined();
  expect(result.body.singleResult.data.user.name).toBe('John Doe');
});
Testing Resolvers in Isolation
While integration tests verify the full GraphQL stack, unit testing resolvers in isolation is crucial for validating business logic. This approach is faster, easier to debug, and helps maintain test coverage.
Resolver Testing Best Practices
- Mock dependencies: Mock data sources, databases, and external services
- Test pure logic separately: Extract complex business logic from resolvers when possible
- Cover all branches: Test success cases, error cases, and edge conditions
- Validate argument handling: Ensure resolvers correctly process and validate arguments
- Test field resolvers: Don't forget to test computed fields and relationship resolvers
// Example of testing a resolver in isolation
const resolvers = {
  Query: {
    user: async (_, { id }, { dataSources }) => {
      const user = await dataSources.userAPI.getUserById(id);
      if (!user) throw new Error('User not found');
      return user;
    }
  }
};

test('user resolver returns user when found', async () => {
  const mockDataSources = {
    userAPI: {
      getUserById: jest.fn().mockResolvedValue({ id: '123', name: 'Jane' })
    }
  };

  const result = await resolvers.Query.user(
    null,
    { id: '123' },
    { dataSources: mockDataSources }
  );

  expect(result.name).toBe('Jane');
  expect(mockDataSources.userAPI.getUserById).toHaveBeenCalledWith('123');
});
Error Handling and Edge Cases
Robust GraphQL APIs need to handle errors gracefully. Testing error scenarios is just as important as testing happy paths.
Common Error Scenarios to Test
- Not found errors: When requested resources don't exist
- Validation errors: Invalid input formats or missing required fields
- Authorization errors: Accessing resources without proper permissions
- Rate limiting: Exceeding query complexity or request limits
- Malformed queries: Syntax errors in GraphQL queries
- Partial errors: When some fields resolve successfully and others fail
# Example query that might trigger partial errors
query {
  user(id: "123") {
    name
    privateData  # This might require auth and fail
    posts {
      title
    }
  }
}
When testing, verify that errors are returned in the standard GraphQL error format with appropriate error codes, messages, and extensions for debugging.
Performance and N+1 Query Testing
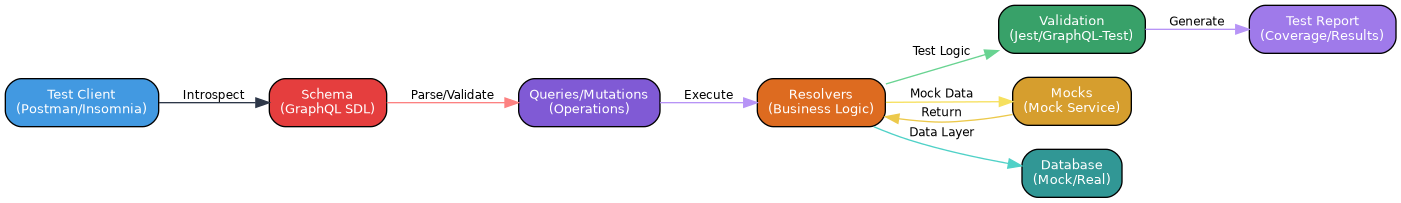
One of the most common performance issues in GraphQL is the N+1 problem, where nested resolvers trigger separate database queries for each item in a list. This can devastate performance with large datasets.
Understanding the N+1 Problem
Solutions to Test
- DataLoader: Batch and cache requests within a single GraphQL request
- Query complexity analysis: Limit query depth and complexity
- Field-level caching: Cache expensive resolver results
- Database query inspection: Monitor actual SQL/NoSQL queries generated
Performance Testing Approach
| Test | What to Measure | Target |
|---|---|---|
| Query response time | End-to-end latency for typical queries | < 200ms for simple queries |
| Database query count | Number of queries executed | Minimize to 1-2 queries for nested data |
| Memory usage | Memory consumption with large result sets | Within acceptable limits |
| Query depth limits | Rejection of overly deep queries | Properly enforced |
| Query complexity limits | Rejection of expensive queries | Properly enforced |
// Example using DataLoader to solve N+1
const DataLoader = require('dataloader');

const postLoader = new DataLoader(async (userIds) => {
  const posts = await db.posts.findAll({ where: { userId: userIds } });
  // Group posts by userId
  const postsByUserId = groupBy(posts, 'userId');
  return userIds.map(id => postsByUserId[id] || []);
});
Security Considerations
GraphQL's flexibility introduces unique security risks that need to be tested explicitly.
Security Tests to Perform
- Query depth limiting: Prevent deeply nested queries that could cause DoS
- Query complexity limiting: Assign costs to fields and reject expensive queries
- Introspection disabling in production: Ensure schema introspection is disabled or restricted
- Field-level authorization: Test that users can only access authorized fields
- Persisted queries: Verify only whitelisted queries are allowed in production
- Rate limiting: Test per-user and per-query rate limits
- Input sanitization: Prevent injection attacks through GraphQL arguments
Important: Never expose full introspection in production environments as it reveals your entire schema to potential attackers.
Automation Strategies
A comprehensive GraphQL testing strategy should include multiple layers of automation.
Testing Pyramid for GraphQL
| Layer | Coverage | Tools | Speed |
|---|---|---|---|
| Schema validation | Contract testing, breaking changes | GraphQL Inspector, graphql-schema-linter | Very fast |
| Unit tests | Resolvers, business logic | Jest, Mocha | Fast |
| Integration tests | Full query execution, auth, data sources | Apollo Server testing, Supertest | Medium |
| End-to-end tests | Real client scenarios, full stack | Playwright, Cypress | Slow |
| Performance tests | Load, stress, query complexity | k6, Artillery, JMeter | Slow |
CI/CD Integration Tips
- Schema checks on PRs: Run GraphQL Inspector to catch breaking changes
- Parallel test execution: Run unit and schema tests in parallel for speed
- Snapshot testing: Use schema snapshots to track changes over time
- Coverage reporting: Track resolver and field coverage
- Automated security scans: Include query depth/complexity validation in CI
# Example GitHub Actions workflow snippet
name: GraphQL Tests
on: [pull_request]
jobs:
  test:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v3
      - name: Schema validation
        run: npx graphql-inspector validate schema.graphql ./queries/**/*.graphql
      - name: Unit tests
        run: npm run test:unit
      - name: Integration tests
        run: npm run test:integration
Real World Example
Let's walk through testing a simple blog GraphQL API to put these concepts together.
Schema Definition
type Query {
  posts(limit: Int, offset: Int): [Post!]!
  post(id: ID!): Post
  author(id: ID!): Author
}

type Mutation {
  createPost(input: CreatePostInput!): Post!
  deletePost(id: ID!): Boolean!
}

type Post {
  id: ID!
  title: String!
  content: String!
  author: Author!
  comments: [Comment!]!
}

type Author {
  id: ID!
  name: String!
  posts: [Post!]!
}

type Comment {
  id: ID!
  text: String!
  author: Author!
}

input CreatePostInput {
  title: String!
  content: String!
  authorId: ID!
}
Testing Checklist
- [ ] Schema: Validate schema parses correctly and all types are consistent
- [ ] Query - posts list: Test with pagination, ensure correct count and ordering
- [ ] Query - nested data: Fetch post with author and comments, verify all resolved
- [ ] Query - N+1: Monitor DB queries, ensure DataLoader is used
- [ ] Mutation - createPost: Test with valid input, verify post created
- [ ] Mutation - validation: Test with missing fields, expect validation errors
- [ ] Error case: Query non-existent post, expect proper null/error handling
- [ ] Authorization: Test protected mutations without auth token
- [ ] Performance: Test deeply nested query, verify complexity limits
Sample Test
describe('Blog GraphQL API', () => {
  test('creates a post successfully', async () => {
    const mutation = gql`
      mutation CreatePost($input: CreatePostInput!) {
        createPost(input: $input) {
          id
          title
          author {
            name
          }
        }
      }
    `;

    const result = await server.executeOperation({
      query: mutation,
      variables: {
        input: {
          title: 'GraphQL Testing',
          content: 'A comprehensive guide',
          authorId: '1'
        }
      },
      contextValue: { user: { id: '1', role: 'author' } }
    });

    expect(result.body.singleResult.errors).toBeUndefined();
    expect(result.body.singleResult.data.createPost.title).toBe('GraphQL Testing');
  });
});
Conclusion
Testing GraphQL APIs requires a shift in mindset from endpoint-based testing to schema-driven, resolver-focused testing. By combining schema validation, isolated resolver tests, comprehensive query/mutation testing, and performance monitoring, you can build confidence in your GraphQL APIs.
Remember that the key to success is layered testing - catch schema issues early, validate business logic in isolation, and verify end-to-end behavior with integration tests. Pay special attention to performance pitfalls like N+1 queries and security concerns like query complexity attacks. With the right strategy and automation in place, you can deliver robust GraphQL APIs that scale safely.
Key Takeaways
- Schema is your contract: Always validate schema changes for backward compatibility using tools like GraphQL Inspector
- Test in layers: Combine unit tests for resolvers with integration tests for full query execution
- Watch for N+1: Use DataLoader and monitor database query counts to prevent performance issues
- Secure by design: Implement and test query depth limits, complexity limits, and field-level authorization
- Automate early: Integrate schema validation and tests into your CI/CD pipeline to catch issues before deployment
- Think in graphs: Test nested relationships and partial error scenarios, not just flat responses
Frequently Asked Questions
Q: Should I test GraphQL the same way as REST? A: No. While some concepts overlap, GraphQL requires additional focus on schema validation, resolver logic, query flexibility, and performance issues like N+1 queries that don't typically occur in REST.
Q: How do I prevent N+1 queries in tests? A: Use query logging or database query counting during tests. Tools like Apollo Server's tracing, or simply counting database calls in mocked data sources, can help you verify that batching is working correctly with DataLoader.
Q: What's the difference between testing resolvers and testing queries? A: Resolver unit tests validate business logic in isolation with mocked dependencies. Query integration tests validate the full execution pipeline including schema validation, middleware, authorization, and actual resolver composition.
Q: Should I disable introspection in production? A: Yes, in most cases. Introspection exposes your entire schema which can aid attackers in understanding your API structure. If you need it for specific clients, restrict it to authenticated users or use persisted queries instead.
Q: How do I test field-level authorization in GraphQL? A: Write tests with different user contexts (roles/permissions) and verify that unauthorized fields return appropriate errors or are filtered out. Test both direct field access and fields accessed through nested queries.


스키마 호환성 검사와 실제 쿼리 실행 검사를 나눈 구성이 좋네요. 특히 일부 필드만 권한 오류가 나는 경우를 별도로 보는 점이 중요해 보입니다. 같은 필드를 직접 조회할 때와 중첩 경로로 조회할 때를 같은 사용자 조건으로 대조하고, DataLoader 테스트에서는 반환값뿐 아니라 실제 DB 호출 수도 확인하면 회귀를 찾기 쉽겠습니다.
ReplyDelete